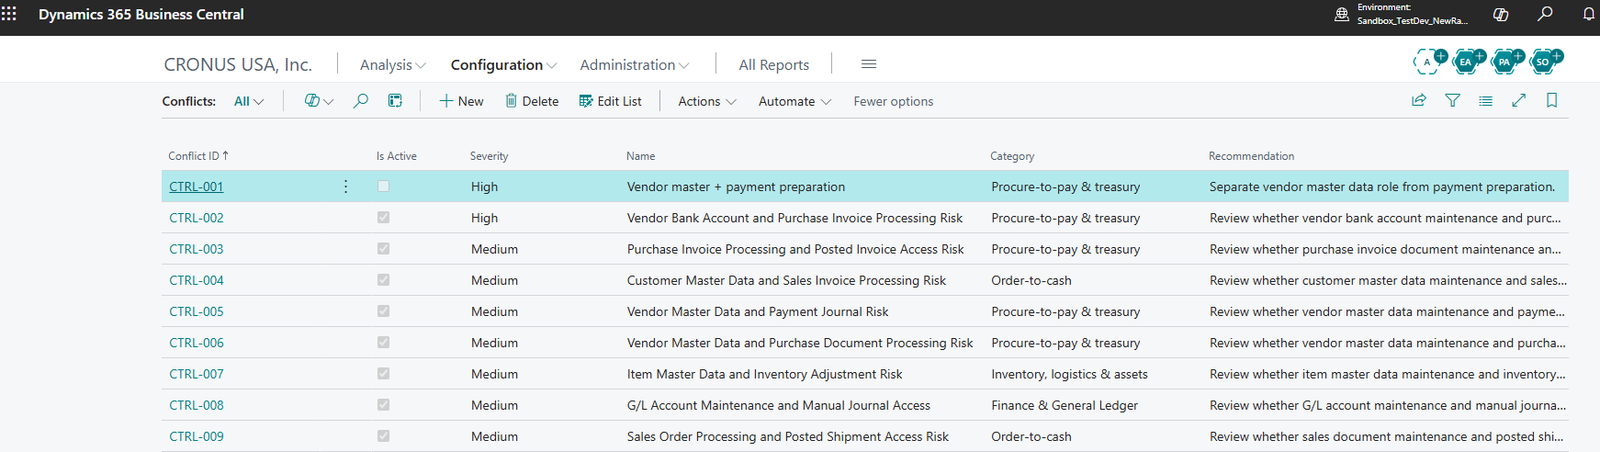
Conflict definitions
Configure SoD controls.
Exploring access governance and Segregation of Duties in Business Central.
A hands-on BC extension for exploring TableData permission patterns, potential SoD conflicts and supporting evidence.
Developed by MJLS Plus · Independent R&D project
The idea: make permission-risk reviews easier to run, understand and discuss.
Capture permissions, check configured SoD patterns and inspect findings—all inside BC.
Capture user assignments and TableData grants.
Combine permission conditions using ANY / ALL.
See why a rule was matched.
Define controls directly in BC.
A short walkthrough recorded in a Business Central sandbox, followed by screenshots of the application.
A brief look at configuring SoD rules, running access analysis and reviewing potential permission conflicts. Recorded in a sandbox environment for R&D demonstration.
Configure SoD controls.
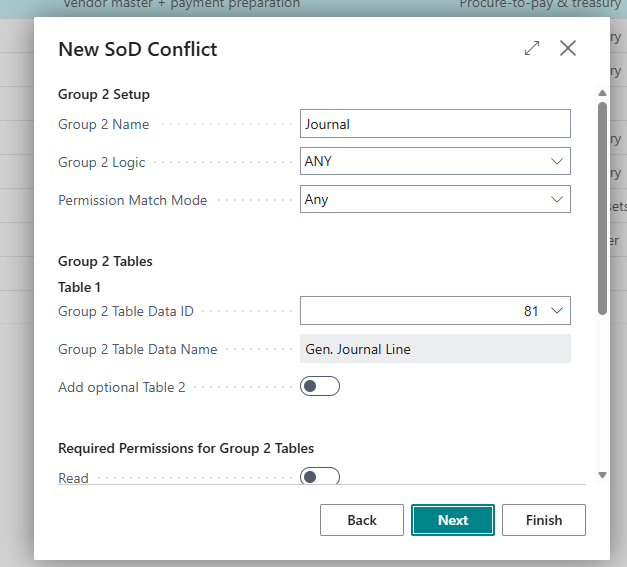
Set up rules in BC.
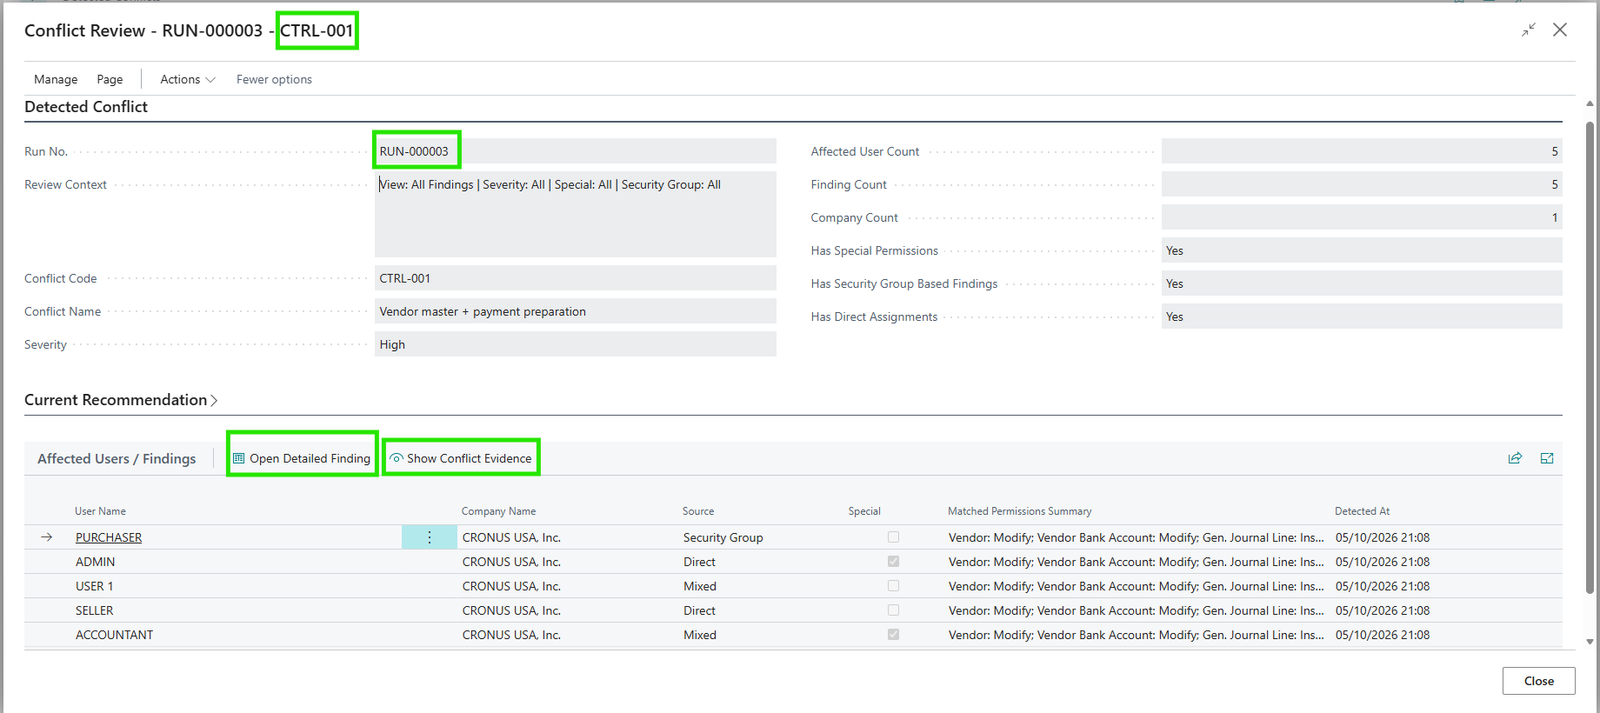
Review flagged risks.
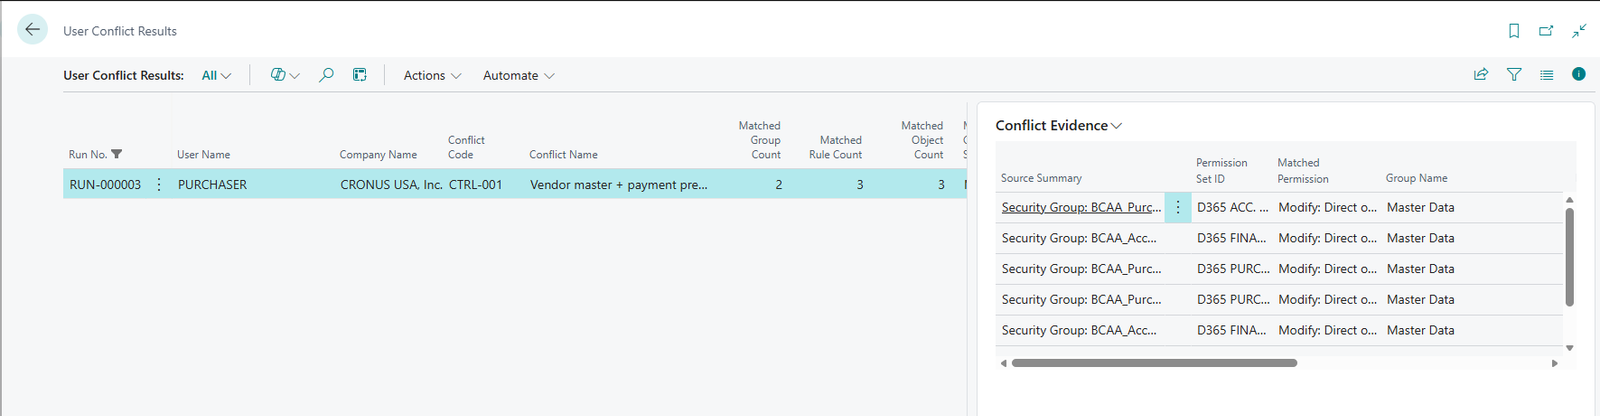
Trace permission evidence.
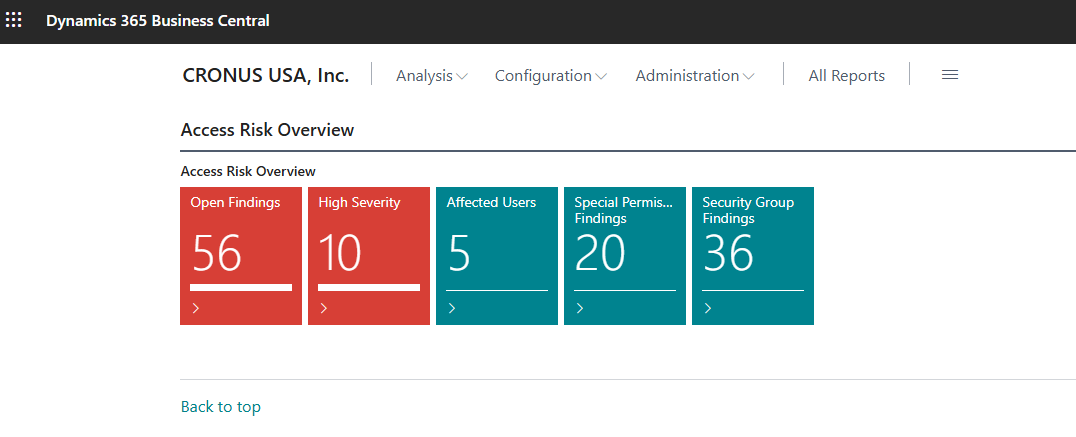
Review analysis results.
Building BCAA surfaced interesting questions about permission semantics, SoD assumptions and testing. I’ll share the practical lessons in a future post.
Tested internally in BC28. Business control definitions and performance in large live environments still need external feedback.
Watch the recorded demo above, or get in touch if you would like to discuss the approach.
BCAA flags configured TableData permission patterns for human review. It does not establish whether a full business process can be executed.
Not a certified security audit or compliance solution. Evaluation is currently limited to R&D/sandbox use.
I enjoyed building BCAA and would welcome candid feedback from BC consultants, AL developers and finance-control specialists.
I'm Marcin, a NAV / Business Central consultant.
I built BC Access Auditor as a personal R&D project to explore permissions and Segregation of Duties in Business Central.
More about my consulting work at mjlsplus.com.
Happy to show BCAA, discuss controls and hear your perspective.
Start a conversation